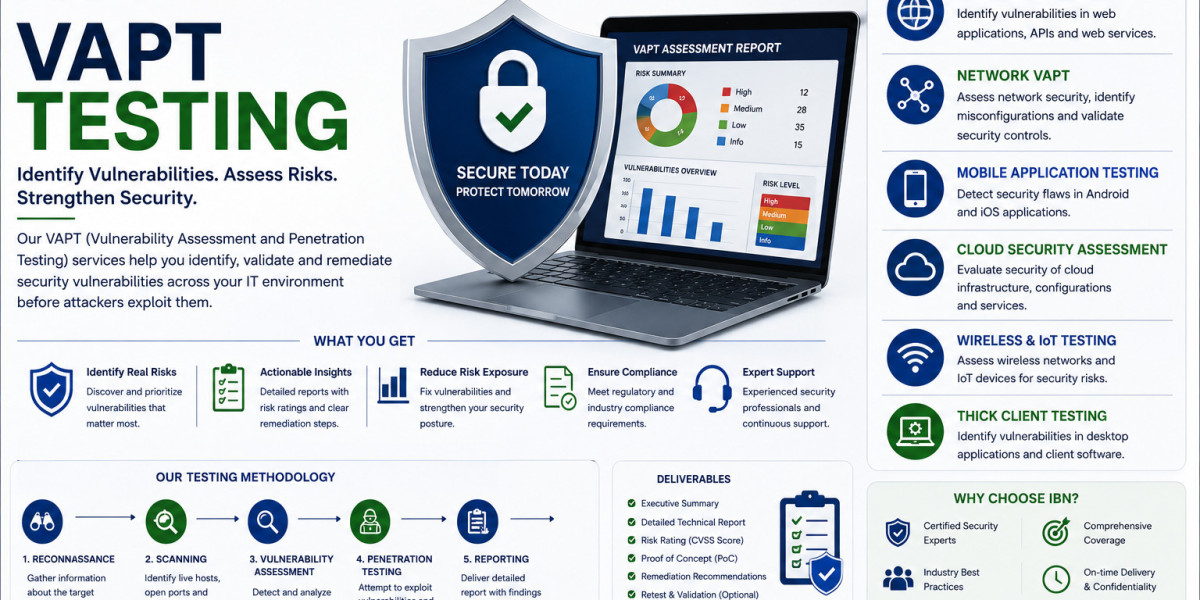
Launching a new financial application involves more than checking whether its features work correctly. Security teams also need to determine whether vulnerabilities could expose accounts, transactions or sensitive information. vulnerability testing services can help FinTech companies in India identify security weaknesses before a new application, payment feature or digital financial product reaches a wider customer base.
Why Testing Before Launch Matters
FinTech products often connect several systems.
A single customer transaction may involve:
- Mobile or web applications
- APIs
- Authentication systems
- Payment gateways
- Databases
- Cloud infrastructure
- Internal services
A vulnerability in one component may create a security pathway into another.
Testing before launch gives security teams an opportunity to identify these weaknesses while changes are still easier to make.
Focus on the Customer Journey
Security testing should follow realistic application workflows.
For example:
Login → Account → Payment → Confirmation → Transaction History
Each step can involve different permissions and backend services.
Testing should determine whether users can manipulate requests or application behavior to access information or functionality they should not have.
APIs Deserve Special Attention
FinTech applications increasingly rely on APIs.
An API may expose account information, transaction functions or payment-related functionality.
Testing should consider:
- Authentication
- Authorization
- Input validation
- Rate controls
- Data exposure
- Error handling
- Business logic
A secure interface should enforce authorization consistently, not simply rely on the front-end application to restrict access.
Testing Infrastructure Alongside Applications
Application security cannot always be separated from infrastructure.
A vulnerable server, exposed administrative interface or weak network control can create additional risk.
vulnerability assessment services can provide broader visibility into infrastructure weaknesses alongside application-focused testing.
This combination can help security teams understand the wider attack surface.
What Happens After a Vulnerability Is Found?
Finding the issue is only the beginning.
The security team should determine:
- What is affected?
- How can the weakness be reached?
- What information or function could be exposed?
- How serious is the risk?
- Who owns remediation?
- How will the fix be verified?
This makes vulnerability testing more useful to development teams.
Testing in Production
FinTech companies should carefully determine whether production systems can be tested.
Some testing techniques may be appropriate in production when controlled, while others should be performed in a dedicated environment.
The scope should clearly define testing windows and restrictions.
Retesting After Fixes
A vulnerability should not simply be marked closed because a developer changed the code.
Retesting can confirm that:
- The original weakness is no longer exploitable
- Authorization works correctly
- The vulnerable endpoint is protected
- The remediation has not introduced another issue
When Should FinTech Companies Test?
Testing can be particularly valuable:
- Before major launches
- After significant application changes
- After architectural changes
- Before onboarding sensitive integrations
- Following serious security incidents
- During periodic security reviews
Build Security Into the Launch Process
For Indian FinTech businesses, vulnerability testing should become part of product development rather than an activity performed only after launch.
When testing is integrated into release planning, security teams can identify weaknesses earlier and developers can remediate them before the application reaches a larger customer base.